The padlock on the code
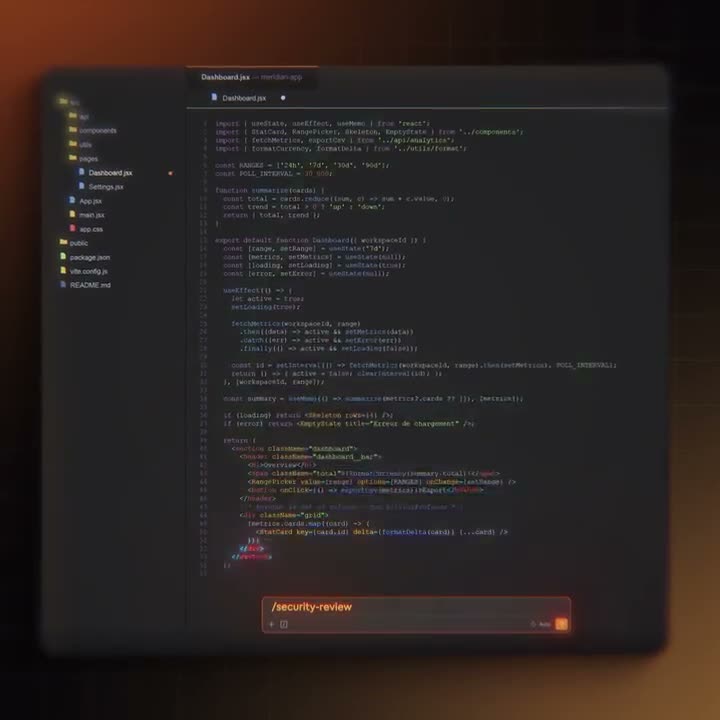
One slash command and the security review runs where the code is written.
We use analytics and ad-measurement cookies (Google, Meta). Nothing is sold, and you can decline.
 Code-to-cloud insurance.

VibeDefend
Learns your project's rules, watches every prompt, lets the agent ship secure code from the start.
The dashboard behind the agent: findings, fixes, policies and reports, on every repo.

The four spots, in full. Sound on, one click.
One slash command and the security review runs where the code is written.
Your AI agent wrote it. The security recipe: a fast install, one line of code.
A secret left in the code is a key left in the door. Protect yourself.
Errors and warnings flagged on the line, before the pull request, then the recipe.
Each stop is a page of its own. Open the one you need.
The documentation walks you through setup, configuration and every option.
Read the docsCybeDefend
Introduction
What CybeDefend does, what happens to your code during a scan, and BLSA, the business logic scanner.
Same data, two surfaces. The platform is the dashboard layer where the scanners (SAST, SCA, IaC, container, secrets, CI/CD), the findings graph, the policies and the compliance reports live. VibeDefend is the agent-time layer that injects the same rules into Claude Code, Cursor, Windsurf and any MCP-compatible client. You can use either independently or both together.
Sign in at eu.cybedefend.com or us.cybedefend.com, OAuth your GitHub / GitLab / Bitbucket / Azure DevOps org, pick a repo, and the first scan starts inside five minutes. No CI step to add, no agent to deploy. The MCP server ships in two regional endpoints (mcp-eu.cybedefend.com/mcp and mcp-us.cybedefend.com/mcp), you only register the one matching your tenant with your AI coding agent.
Source is fetched, analysed and the results are stored in the region you pick at signup (EU = Paris, US = Iowa). EU and US tenants are isolated; nothing is replicated across regions. Source itself is deleted immediately after analysis, only findings, summaries and graph metadata are persisted.
Yes, on the Enterprise plan. We ship a single OCI image, a Helm chart and an air-gapped tarball. Same feature parity as the SaaS, including Cybe AutoFix and the MCP server, you just point your agent at your in-cluster MCP URL instead of the regional mcp-eu.cybedefend.com / mcp-us.cybedefend.com hosts.
SAST: TypeScript / JavaScript, Python, Go, Java / Kotlin, C# / .NET, Ruby, Rust, PHP, plus framework-aware rules for Next.js, NestJS, Django, FastAPI, Spring, Rails, Laravel. IaC: Terraform / OpenTofu, Kubernetes, Helm, CloudFormation, Pulumi, Ansible, CDKTF. Container: any OCI image (Alpine, Debian, Ubuntu, RHEL/UBI base layers, npm, PyPI, Maven, Go, Cargo, NuGet, Composer dependencies). CI/CD: GitHub Actions, GitLab CI, Jenkinsfile.
One command wires every coding agent on your machine to CybeDefend: your business rules, your compliance frameworks, and guards that block destructive calls before they fire.
npx -y @cybedefend/vibedefend@latest install Claude Code
 Cursor
 OpenAI Codex
 Windsurf
 VS Code Copilot