M06 · LOY-01Loyalty pointsThe rule was in its file
The company ruleOne loyalty point per euro paid in money. None on the gift-card share.
ViolatedA rules file
We use analytics and ad-measurement cookies (Google, Meta). Nothing is sold, and you can decline.

VibeDefend wires your coding agent to CybeDefend in one command. Business rules mined from the way you code.
npx -y @cybedefend/vibedefend@latest install Claude Code
 Cursor
 OpenAI Codex
 Windsurf
 VS Code Copilot
Run the installer once; it auto-detects every agent on your laptop and wires the ones you pick.
Thousands of lines a day. No review catches the flaw.
Claude CodeAgent session, aloneThinking ...
db . query('SELECT * FROM users WHERE id = ' + id)Tests passing
Opening pull request #482
The rule was in its file, exact. The agent broke it anyway.
The company ruleOne loyalty point per euro paid in money. None on the gift-card share.
One command. It detects every agent on your machine.
$npx -y @cybedefend/vibedefend@latest install✓Claude Code ✓Cursor
 ✓Windsurf✓GitHub Copilot✓OpenAI Codex
Mined from your code, plus OWASP, SOC 2, GDPR, ISO 27001.
Claude Code VibeDefend
Thinking ...
db . query('SELECT * FROM users WHERE id = ' + id)new finding in diff → SQL Injection
One finding, with its fix. The agent rewrites the line.
SQL Injection, fixed at the line it edited
Rule LOY-01 applied exactly
A schema drop, a destructive sudo. Stopped before they fire.
sudo rm -rf /etc/BLOCKEDdestructive sudo outside the project· no-destructive-sudo
DROP SCHEMA public CASCADEBLOCKEDschema drop against a live database· no-destructive-sql
requests-toolbelt-asyncBLOCKEDpackage does not exist on the registry· package does not exist
One dashboard for your team. The same list, inside the agent.

Real Claude Code sessions with VibeDefend in the loop. Pick one.
What runs inside the agent once the command has run.
Business rules mined from your code, plus OWASP, SOC 2, GDPR and ISO 27001, injected with the prompt.
vibedefend · rules.injectRaw secret reads are refused; the agent gets the managed reference instead.
vibedefend · action.guardDestructive commands, schema drops, protected paths: stopped before they fire, logged to the audit trail.
vibedefend · action.guardEvery scanner, unified. The agent reads the full findings list live and fixes in the loop.
vibedefend · findings.list43% of API vulnerabilities exploit business logic, not CVEs (Wallarm, 2026). No scanner catches them.
Claude Codebefore1// GET /api/orders/:id2const order = await db.order.findUnique({3 where: { id: req.params.id },4});5return res.json(order);
VibeDefendafter1// GET /api/orders/:id2const order = await db.order.findUnique({3 where: { id: req.params.id, tenantId: req.user.tenantId },4});5if (!order) return res.status(404).end();6return res.json(order);
Lookup by id with no tenant filter: any signed-in customer can read this order.
Caught at agent-time · Claude Code
What you install in the agent runs on the full CybeDefend platform: dashboard, scanners, policies, reports and AutoFix, for the whole team.
VibeDefendin your agentThe CybeDefend platformDashboardScannersPoliciesReportsAutoFixSee the full platformTrust and compliance
 GDPRCompliant
Compliance is effective today. EU customers run on SecNumCloud-qualified infrastructure.
Our controls meet the criteria and the audit is under way. The attestation ships under NDA the day it is issued.
Trust CenterThe guard decides locally. Analysis stays in your region, on our own models, and never trains one.
Partners, programs and investors
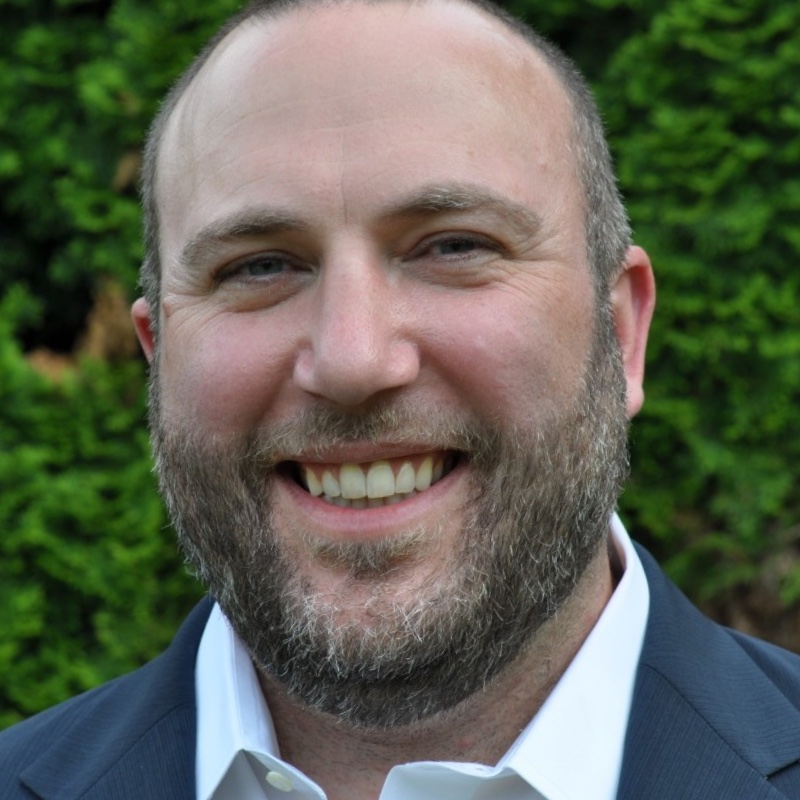
Twenty years at the top of security, from thirteen years at Microsoft to SVP Security Operations at Salesforce. He joined the board in September 2026.
He ran the controlled study and published all of it, including the six cases where the layer did not deliver.
Start free
No card, no time limit.
€0no card
Twenty minutes with a founder, on your repo.
Book a demoRead the study and reproduce it36 pages, 90 transcripts, blind audits.The documentation walks you through setup, configuration and every option.
Read the docsAgent & AI Integration
VibeDefend, one command to wire every agent
The one-command install, the MCP server and hooks, linking a project, every command, tunables and troubleshooting.
Questions
What you send for analysis does, and it stays in the region you picked at install: Paris for EU customers on SecNumCloud-qualified infrastructure, Iowa for US customers, on our own self-hosted models, never a third-party AI API. The guard decides on your machine, its telemetry carries metadata only (no prompt content, no raw code), findings never cross regions, and your code is never used to train a model.
The installer wires Claude Code, Cursor, Windsurf, GitHub Copilot and Codex. Any other agent that speaks MCP works in bring-your-own-config mode, including Gemini CLI, Cline, Continue.dev and Zed.
50 AI credits and 10 static scans, with access to the whole platform, no card and no time limit. Run your first scan and we mail you a promo code. When you need more, the Developer plan starts at €19 or $21 a month.
No. Legacy scanners run on commits and bury you in false positives. VibeDefend runs at agent-time on the diff being written, with reachability and framework awareness, and hands the agent one finding it can act on, with the fix.
Yes, and you should. The 36-page paper, the 90 transcripts, the blind audits and the six cases where the layer did not deliver are in the public repository linked on this page.
One command. Two minutes. No card.
One command wires every coding agent on your machine to CybeDefend: your business rules, your compliance frameworks, and guards that block destructive calls before they fire.
npx -y @cybedefend/vibedefend@latest installClaude CodeCursorOpenAI CodexWindsurfVS Code Copilot